New Cybersecurity Threat: Your Private Life Going Public, Including Your Deleted Messages, Photos, Videos and Search History?
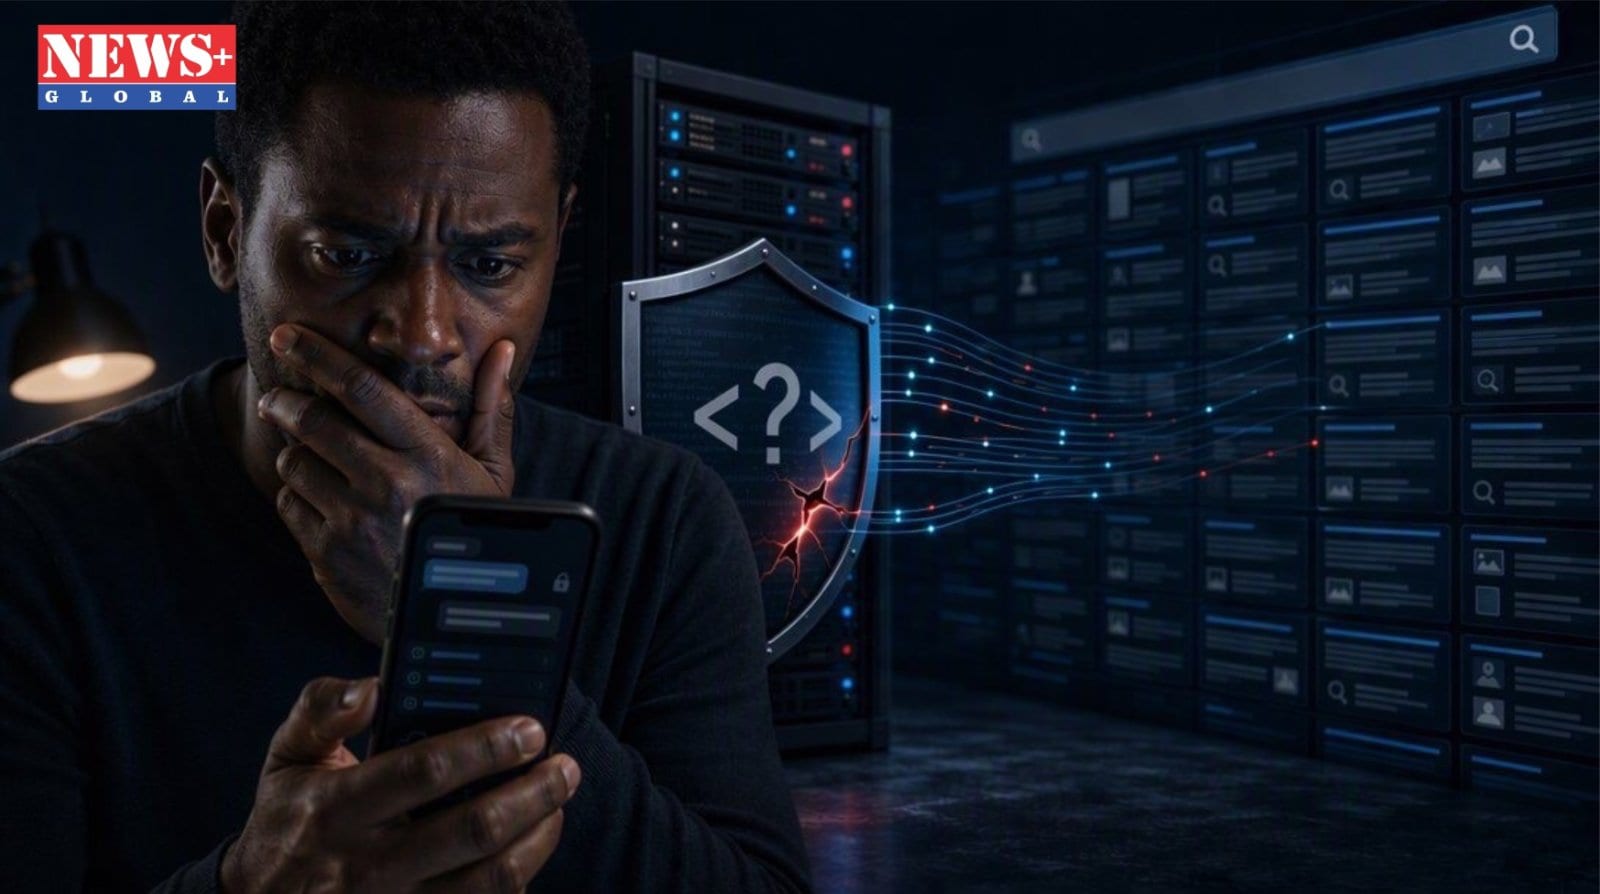
A growing warning about artificial intelligence, data exposure and cybersecurity predicts that private digital information could become publicly searchable within the next 18 months. The claim includes private messages, text conversations, browser histories, network searches, adult-content records and photographs believed to have been deleted from smartphones.
The warning, circulated alongside a video said to demonstrate the recovery of deleted iPhone photographs through Claude, has not been independently verified. However, it reflects broader concerns among cybersecurity experts about data retention, cloud backups, device forensics and the expanding ability of artificial-intelligence systems to process large personal datasets.
The scenario described is not necessarily one of a total infrastructure collapse. Instead, it suggests a quieter but potentially profound crisis in which private details become exposed, while short-term disruptions affect businesses and public services. Possible consequences could include corrupted bank records, confused financial reporting and failures involving refrigerated goods if store freezers lose power or systems are compromised.
The central concern is the possible end of privacy as people currently understand it. If private communications and personal records become searchable, existing power structures could respond by imposing stricter controls on online communication, ostensibly to protect citizens but also to protect governments, corporations and influential individuals from exposure.
The warning argues that such disclosures could affect far more than political leaders and wealthy financiers. Private communications involving academic fraud, professional misconduct, financial arrangements and other sensitive activities could become accessible to anyone with the ability to search the underlying data.
One example cited involves a woman who allegedly completed tests and coursework for wealthy families’ children for approximately $150 an hour. The account claims that she accumulated several degrees through this work over a period of five years. The allegation has not been independently confirmed.
Other potentially damaging searches could include what a manager said privately about employees, what a teacher told a school principal about a student, how a nonprofit spent donated funds, how a campaign manager handled money, how much an influencer actually earns, what parents searched for online about their children or how pandemic-relief funds were used.
The warning also refers to government records, financial networks and publicly discussed criminal-investigation files. It argues that the issue is not simply whether society reaches “the end,” but whether the concept of a private life survives in its current form.
Against that broader backdrop, a separate cybersecurity alert identifies vulnerabilities referred to as PHP2Shell. According to the supplied material, the flaws are tracked as CVE-2026-109618 and CVE-2026-109619 and allow unauthenticated attackers to execute code on servers using PHP. PHP reportedly issued fixes on October 21, 2026.
The potential exposure extends beyond ordinary web servers because PHP is included in firewalls, network-attached storage devices, hosting-control panels, cloud platforms and enterprise software. The affected products reportedly include Palo Alto Networks PAN-OS versions 12.2 through 10.2, Panorama and certain WildFire appliances; Cisco Expressway and URWB products; Citrix NetScaler; F5 BIG-IP; Check Point Force, Spark and Cloud Firewall interfaces; and Broadcom Carbon Black App Control Server.
The list also identifies QNAP systems running affected versions of QTS, QuTS hero, QuTScloud, Note Station, QuMagie, QNE, QVR Surveillance and TVR OS. Synology’s end-of-life PHP 7.3 package and Sophos’s MyUTM licensing portal were also cited. Sophos reportedly took the licensing portal offline on October 21 to perform updates.
Several products are said to have fixes available. These include Okta Access Gateway 2026.44.0, Broadcom Symantec Endpoint Protection Manager releases 14.3.27716.10000 and 14.4.494.0000, Tenable Security Center and Enclave Security, Checkmk Appliance, Netgate pfSense, OPNsense, Synology PHP packages, Unraid OS 7.3.4, Delta Controls enteliWEB and FileCloud Server 23.263.2.
Hosting platforms and control panels listed as patched include cPanel and WHM, Plesk, DirectAdmin, HestiaCP, aaPanel, CloudLinux and TuxCare. Fixed PHP packages have also reportedly been issued for Ubuntu, Debian, Red Hat Enterprise Linux 9, SUSE Linux Enterprise, Arch Linux, Gentoo, FreeBSD ports, NixOS and Homebrew.
The alert further says patched runtimes are available on AWS Elastic Beanstalk, Azure App Service for Linux, Google App Engine Standard, Heroku, Laravel Cloud and Vapor, Pantheon, Upsun, Scalingo, Kinsta and WP Engine. N-able reportedly completed fixes across its hosted platforms on October 22, while customers operating their own containers on Cloud Run or App Engine Flexible may need to rebuild them.
Some vendors remain under investigation, including parts of Cisco, Fortinet, Broadcom, Juniper and several NAS manufacturers. Other products are reportedly not affected, including numerous Fortinet security platforms, Palo Alto’s Cloud NGFW and Prisma Access, Cisco ISE and Umbrella, Sophos UTM and Firewall, and Paessler’s PRTG products.
Security professionals and business owners are advised to patch PHP wherever it is controlled, restart PHP workers, apply appliance fixes as soon as they become available, keep management interfaces off the public internet and restrict access to trusted addresses. Organizations are also advised to investigate possible compromise from October 17, identified in the supplied alert as the earliest known attack date, and to monitor vendor advisories because patch information may change daily.
Comments
Join the conversation. Please keep it respectful.
No comments yet — be the first to share your thoughts.